Amazon S3
Stores the static HTML, CSS, JavaScript, SVG, and error page. Public access remains blocked.
The design separates public delivery from private storage and gives every AWS service one clear responsibility.
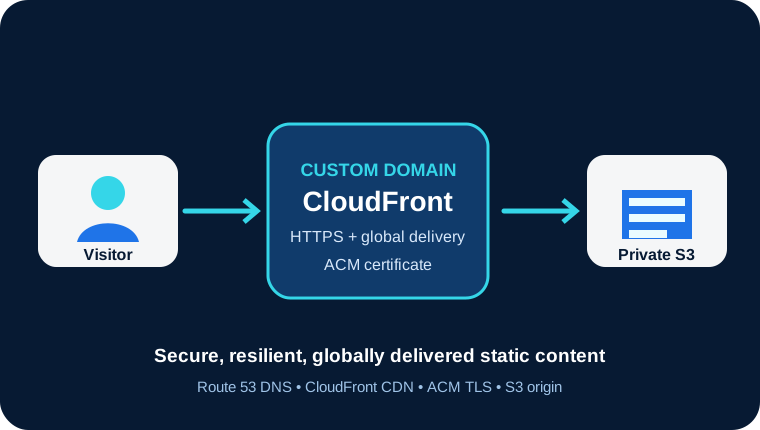
A visitor enters the custom domain. DNS directs the request to CloudFront, which provides HTTPS and retrieves approved content from the private S3 origin.
Stores the static HTML, CSS, JavaScript, SVG, and error page. Public access remains blocked.
Provides the public delivery endpoint, caching, HTTPS enforcement, and controlled origin access.
Connects the registered domain to the CloudFront distribution through DNS alias records.
Issues and manages the certificate that proves the domain identity and enables encrypted traffic.